

Enumeration
Run Nmap Scan
Update Hostname
View Website
Directory Bruteforcing (Run Gobuster)
Enumerating Subdomain Information
Subdomain Bruteforcing (Failed)
Inspecting Website Code
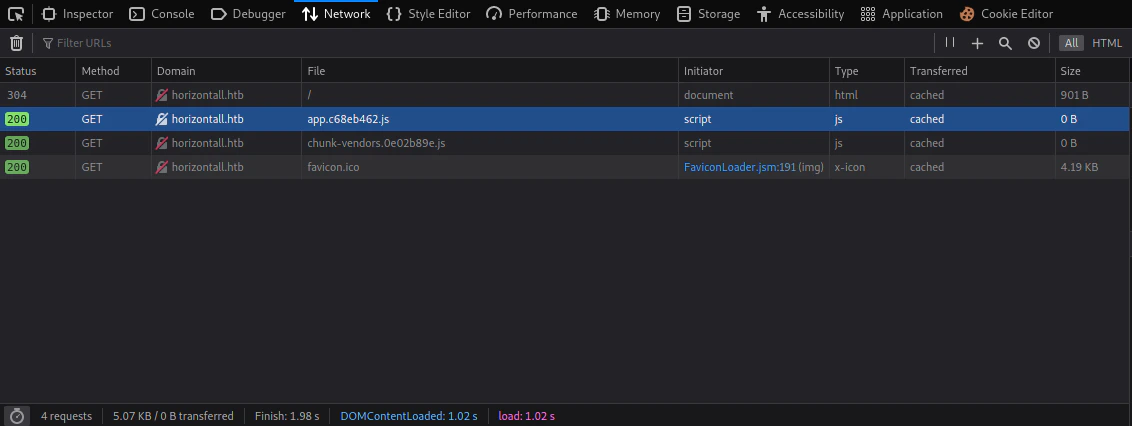
.js files. We are going to inspect the app file, so we can get any additional information.
http://api-prod.horizontall.htb/reviews that we can enumerate.
Update Hostname
api-prod.horizontall.htb was included in the hostname
api-prod website directory bruteforcing (Run Gobuster)
Exploitation
Strapi Enumeration
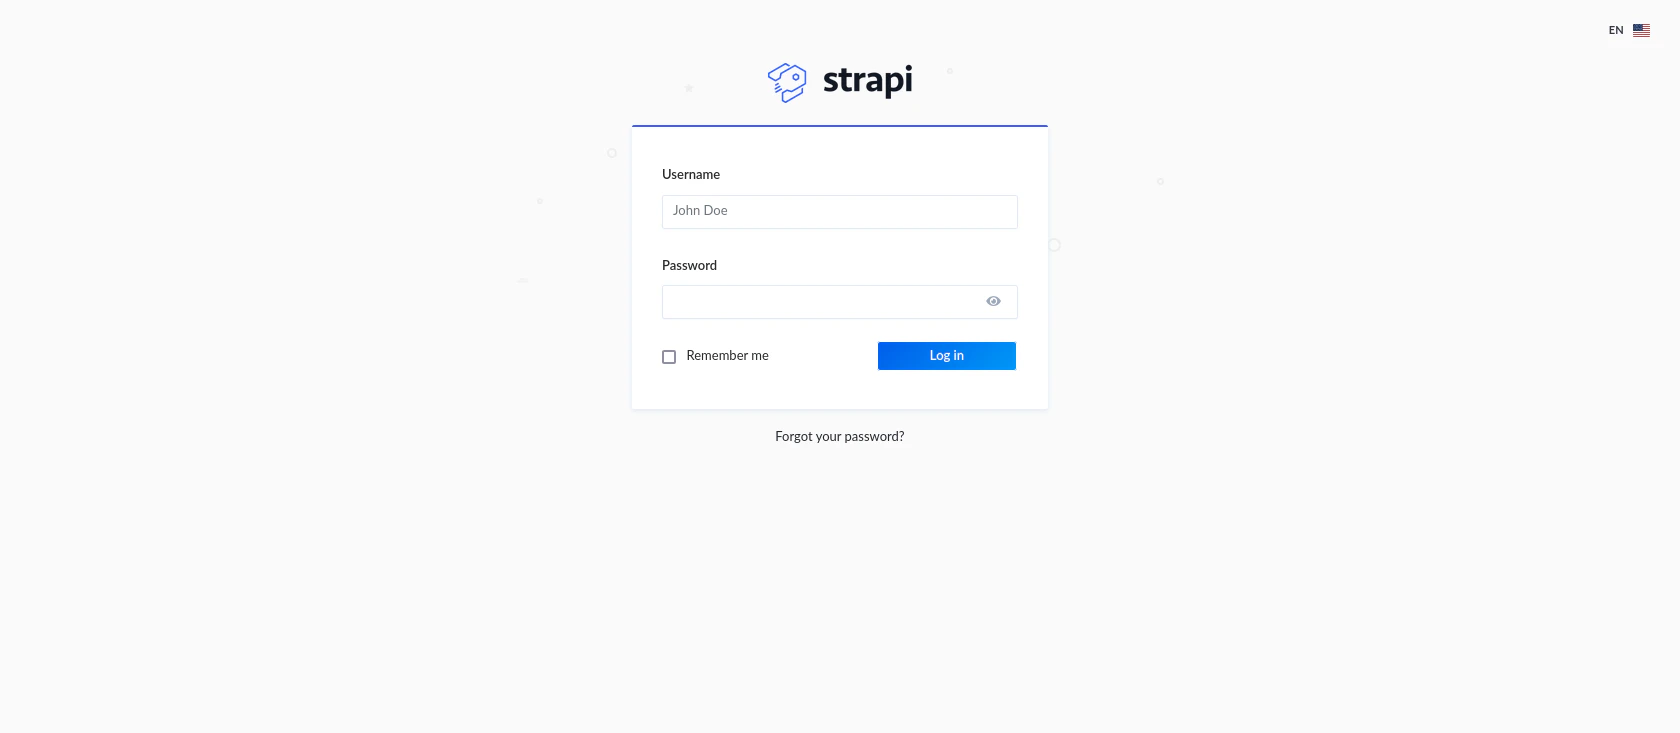
/admin , we get this login page.
Strapi - Open source Node.js Headless CMS 🚀
It’s a CMS application built in node js.
Finding Exploit
strapi version is either 17.4 or 17.7, we could exploit this vulnerability.
Finding version no.
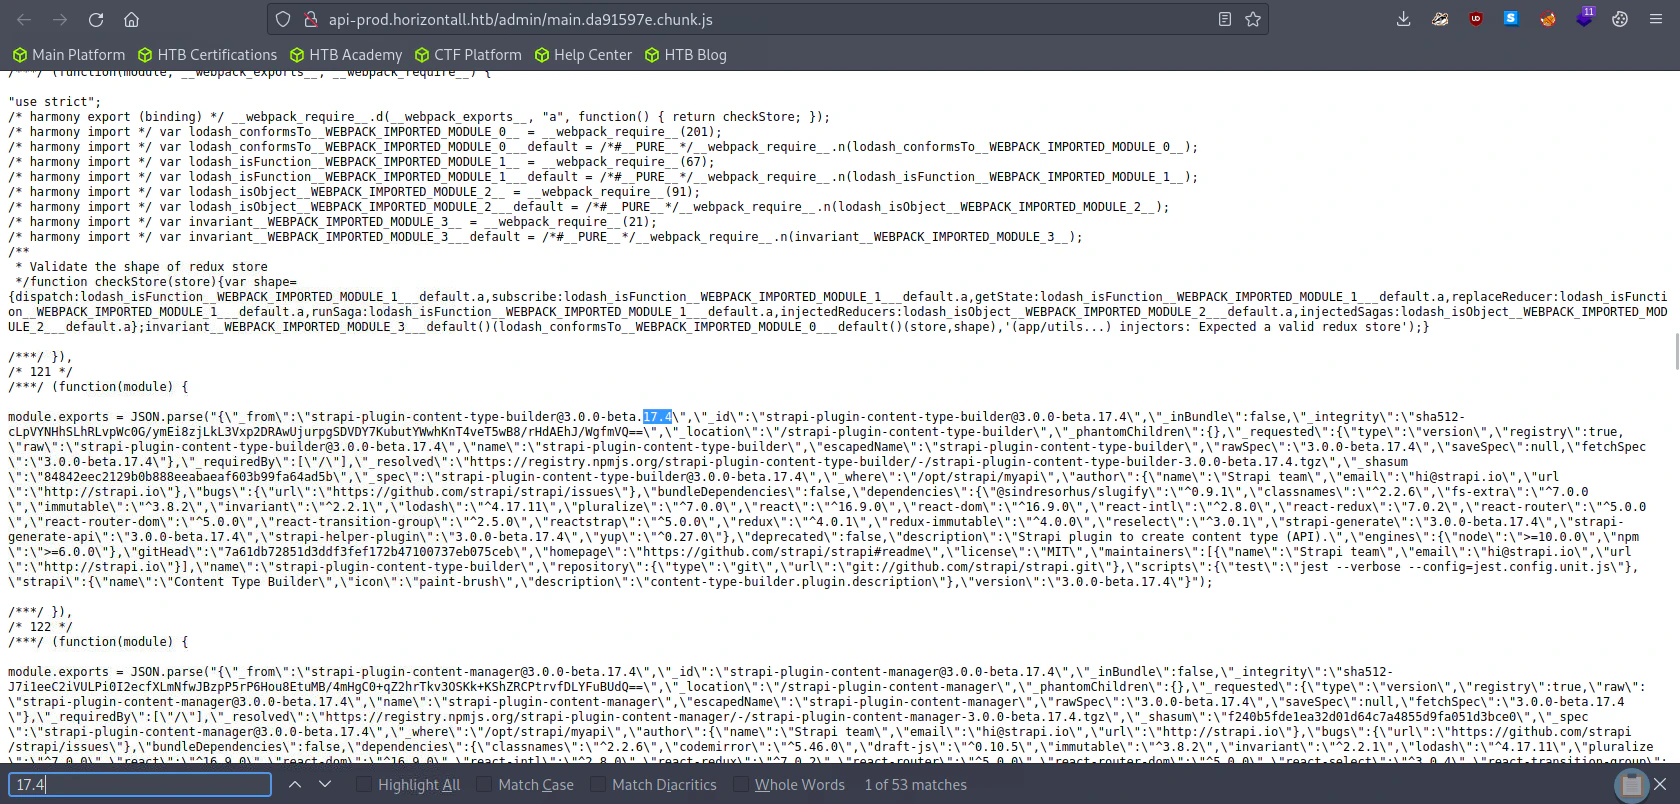
beta.17.4
Using CVE-2019-19609
Exploit
Using Python Reverse Shell (Failed)
First I’m going to check if the target system has python installedUsing Telnet Reverse Shell
Privilege Escalation
Finding Credentials from MySQL Configuration File (Failed)
Enumerating Network Information
Port Forwarding using SSH
Checking SSH config in the target system
.ssh/authorized_keys path. Meaning in ~/.ssh/authorized_keys path.
Generating SSH Key
id_ed25519.pub file (SSH public key).
Download the public key inside the Specified PATH
Port Forward 8000 to Our System.
Enumerating Localhost:8000
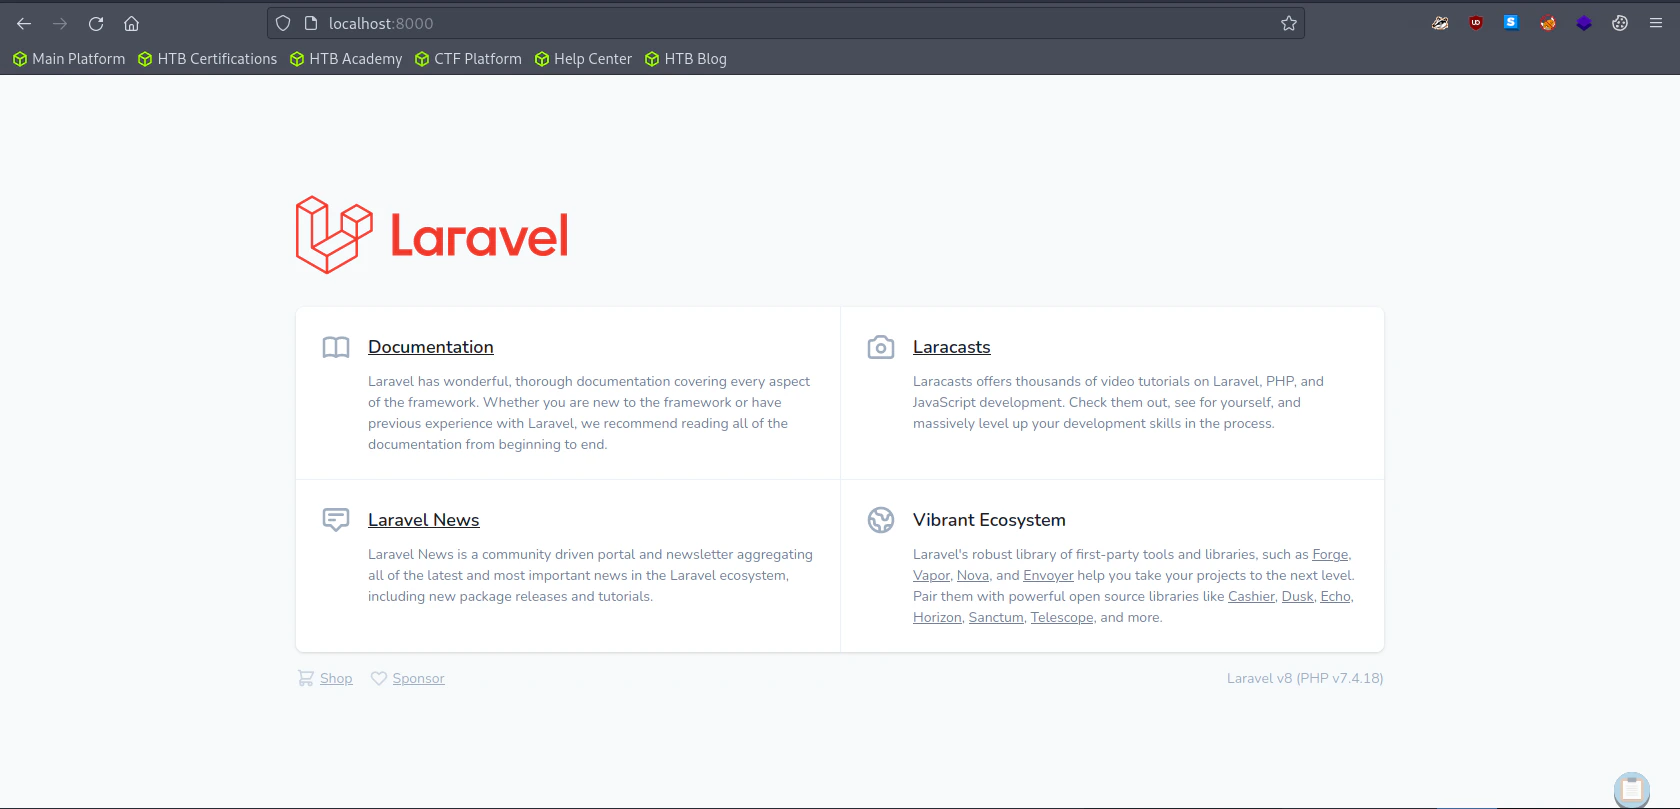
localhost:8000 directory bruteforcing (Run Gobuster)
Exploiting the Vulnerability
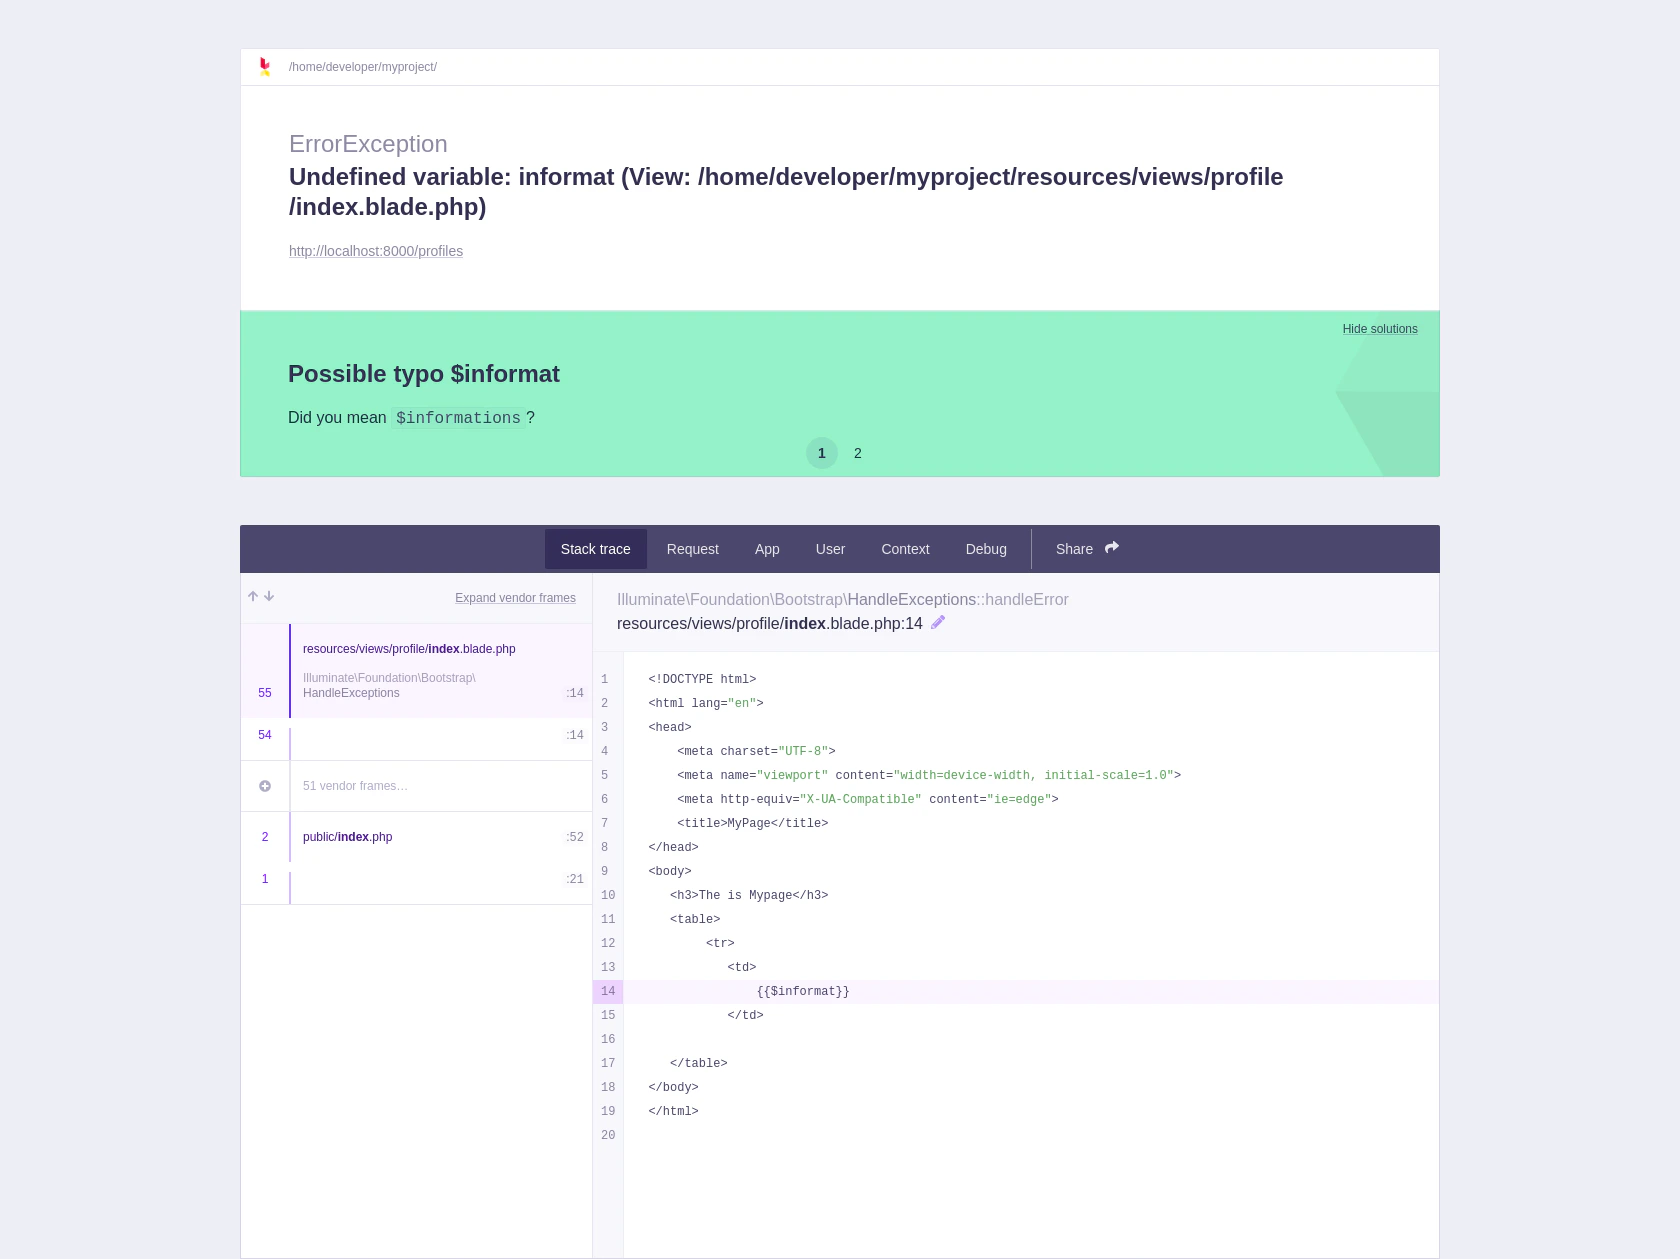
/profiles , here we can see an error occured and know this is a debug menu.
Finding Laravel debug mode exploit in google, I found an interesting website.
Laravel up to v8.4.2 debug mode: Remote code execution
It requires version less than 8.4.2 which can be used to exploit our target system as the target system is using Laravel v8. (Look closely in the Laravel default website)
Generating a Reverse Shell
Online - Reverse Shell Generator/tmp folder using wget and give execution permission using chmod +x reverse.sh
Using CVE-2021-3129
https://github.com/nth347/CVE-2021-3129_exploit Execute the exploit in our machine, but don’t forget to maintain the SSH Port Forwarding connection.Listen to Reverse Shell and Exploit
References
- https://docs-v3.strapi.io/developer-docs/latest/setup-deployment-guides/configurations.html#required-configurations
- https://www.ibm.com/docs/en/ioc/1.6.0?topic=servers-updating-ssh-configuration
- https://unix.stackexchange.com/questions/36540/why-am-i-still-getting-a-password-prompt-with-ssh-with-public-key-authentication
- https://0xdf.gitlab.io/2022/02/05/htb-horizontall.html#shell-as-root
- https://www.ambionics.io/blog/laravel-debug-rce
- https://github.com/nth347/CVE-2021-3129_exploit